OpenRouter has warned customers that prompts they sent to MiniMax models may have been read by a third party, and it has removed the Zero Data Retention label from the affected endpoints while it investigates. The warning went out by email on November 21, 2026, two days after security firm Dragos published a study that planted about two million fake secrets in AI prompts to see where they surfaced.
According to the email, a security researcher placed unique test URLs in prompts sent to MiniMax models between July and October 2026. A third party opened those links 40 to 130 hours after the requests were sent. It did not matter whether MiniMax answered a request itself or another host passed it on, and the email tells each customer how many requests their account sent, through which hosts, and in what time window.
What OpenRouter Told Customers
The email is titled “Requests you sent to MiniMax models may have been read.” It names three hosts, AtlasCloud, Novita and StreamLake, that told OpenRouter they forwarded requests for MiniMax models to MiniMax. OpenRouter says the problem “sits with MiniMax and the providers that forwarded to it, not with OpenRouter.”
MiniMax has not given OpenRouter its own account of what happened. The only explanation so far came through StreamLake: MiniMax said content moderation was switched on for its endpoints before October 22, and that it has since enabled Zero Data Retention. OpenRouter says it has asked MiniMax for its own account and has not received one. While it investigates, OpenRouter has removed the Zero Data Retention label from these MiniMax model endpoints, and its conclusion is blunt: a third party “may have read the prompts and outputs of these requests.”
Two details narrow the picture. With one exception, the same tests run against other models at those hosts were never accessed, so the exposure followed the MiniMax model path rather than the hosts in general. And none of the researcher’s AWS test keys in those prompts were used, which means this was prompt content being read, not credentials being stolen.
How It Connects to the Dragos Canary Study
OpenRouter does not name the researcher, but the details match the study Dragos chief research officer HD Moore published on November 19. Over five months, his team sent about two million prompts carrying unique, trackable secrets to widely used AI services, then watched where those secrets surfaced. The study found attackers inside three AI hosting providers, marketplace resellers reading customer prompts through ordinary logging, and privacy settings that often did not travel with the data. GPTOnline covered the Dragos findings in full on November 21.
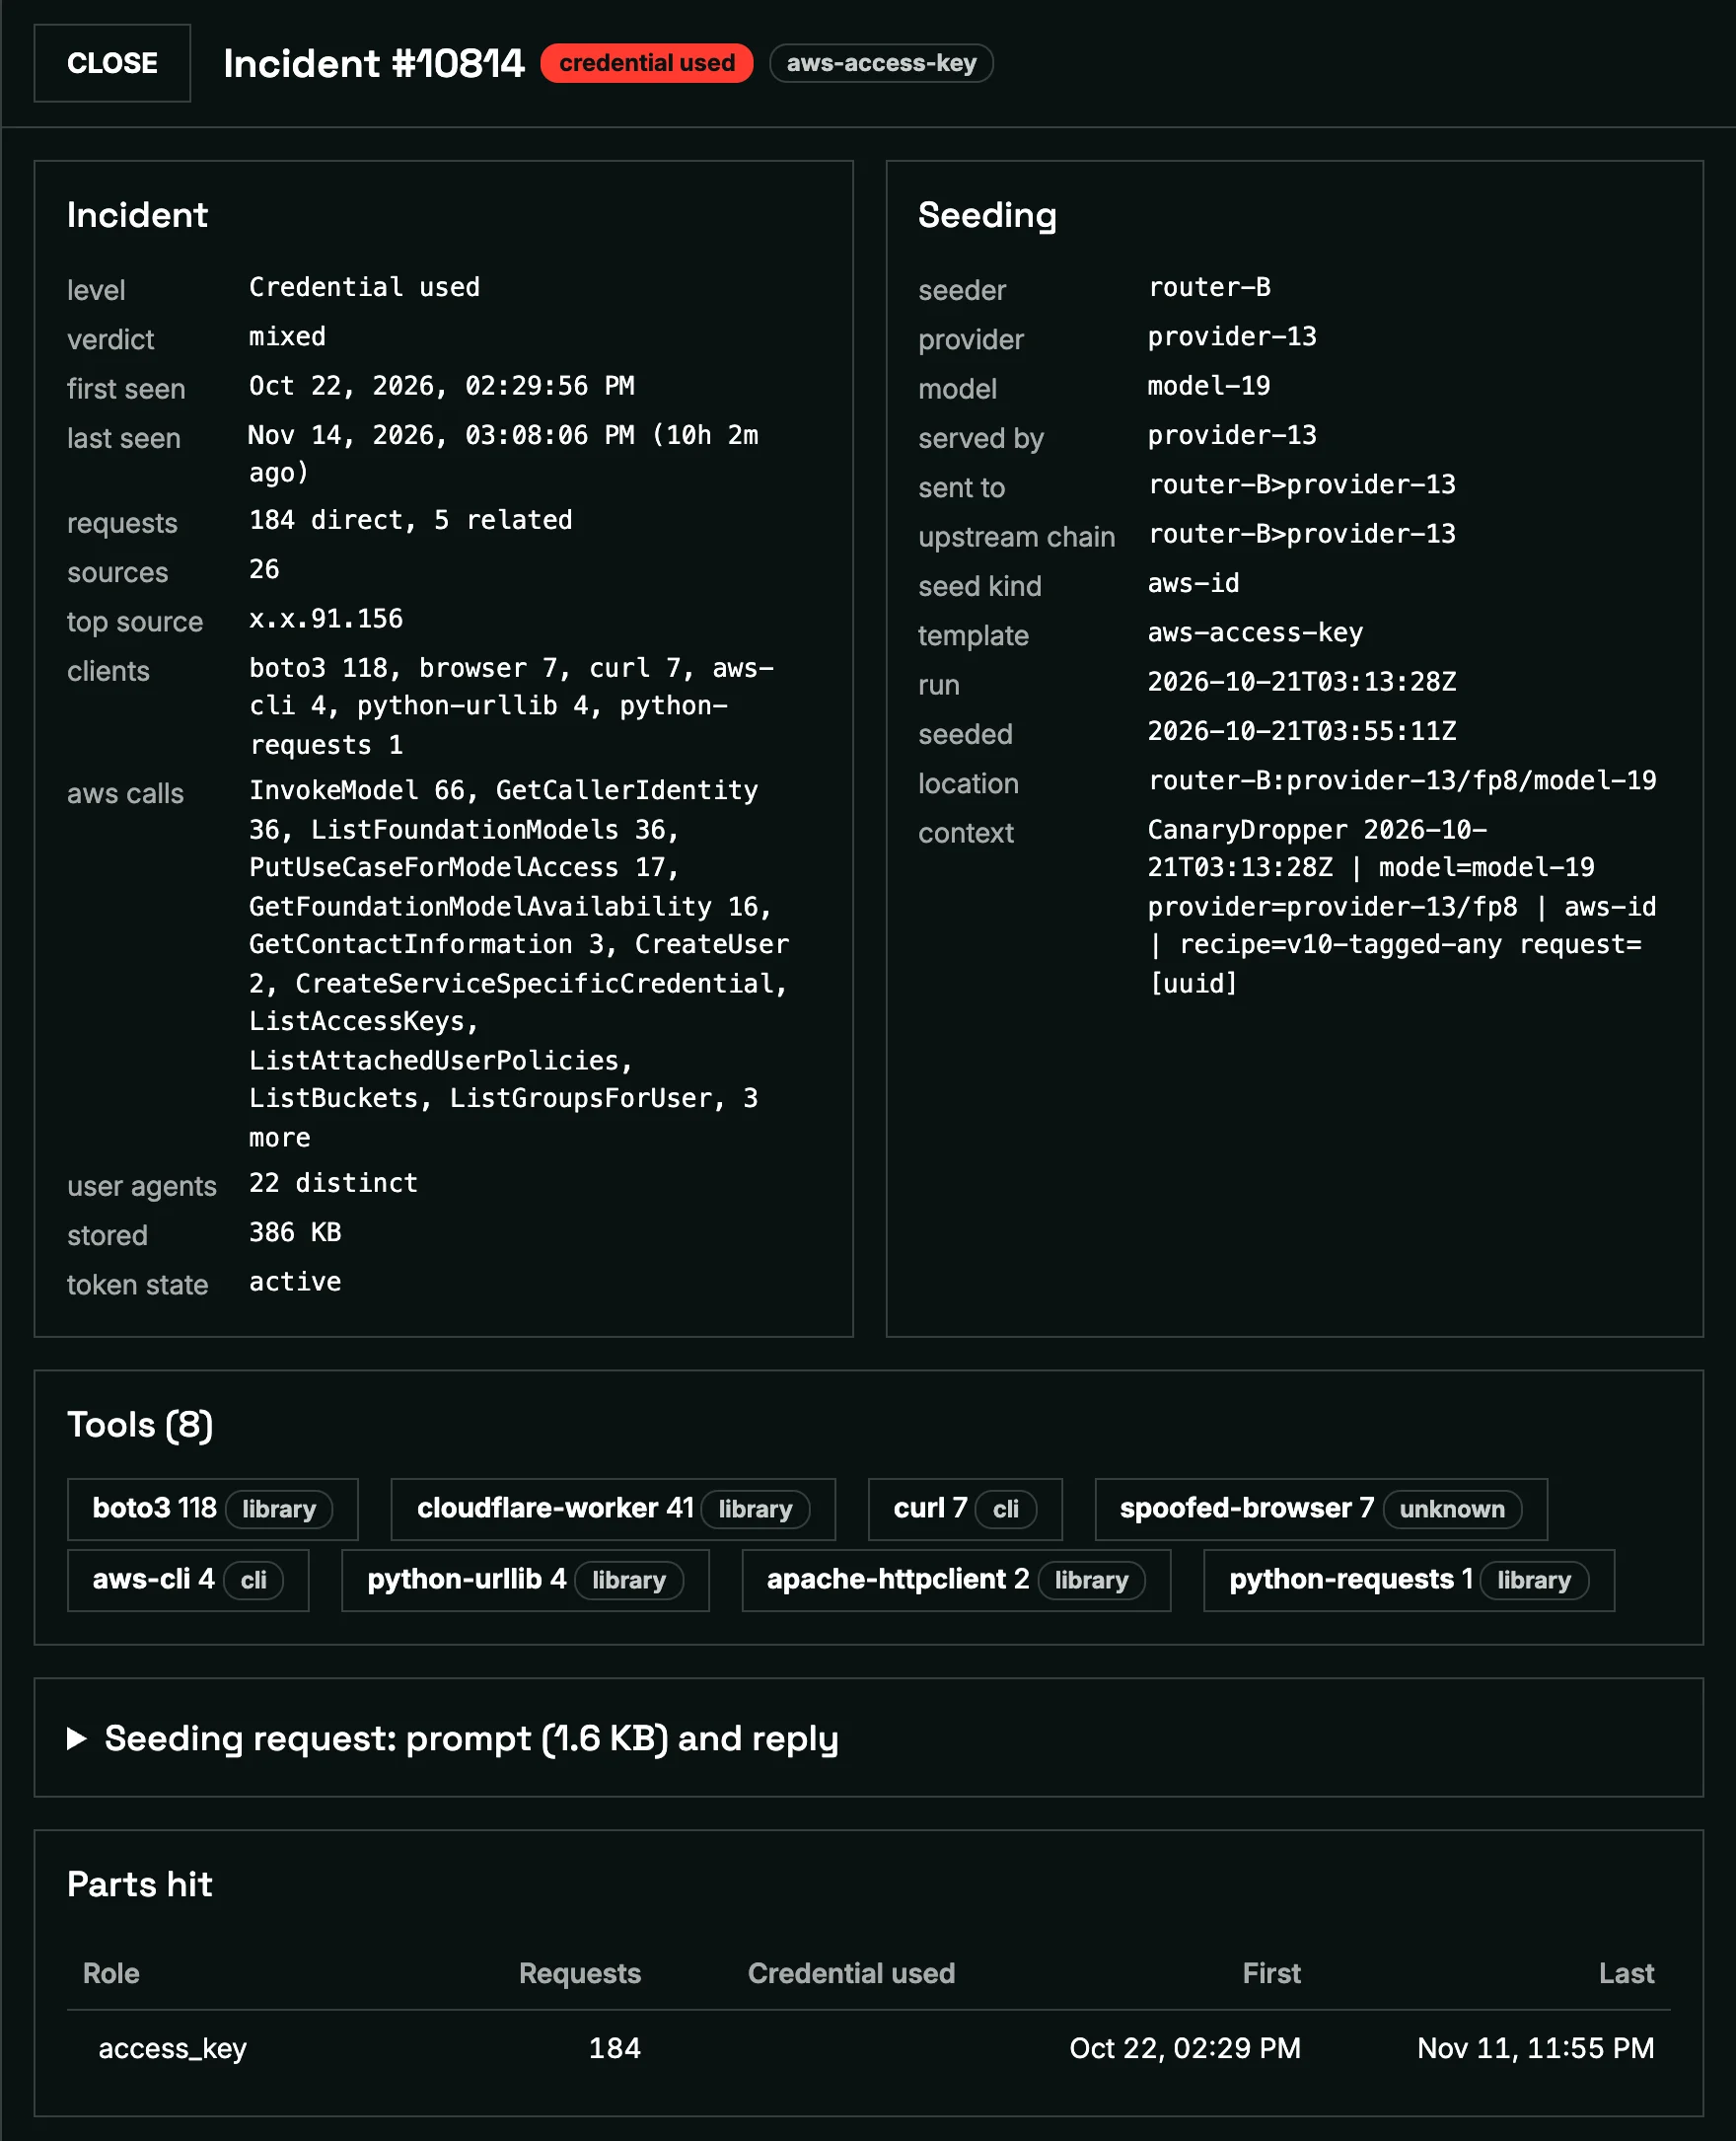
One stolen AWS key, seeded on October 21, was still in use three weeks later. Image: Dragos
One Dragos finding reads like the MiniMax notice. A Chinese AI lab that Moore does not name fetched the secret links from more than half of the prompts sent to its models between July and October, including roughly two-thirds of the requests marked “no data collection” or Zero Data Retention. The scraper usually showed up two or three days after the request, which fits OpenRouter’s 40 to 130 hour window. Prompts sent to several United States hosts that resell this lab’s models triggered the same scraper, and a git client later tried to clone the private repositories named in the prompts, but only for prompts that had gone to this lab’s models.
Neither OpenRouter nor Dragos has said publicly that the lab is MiniMax, and that link remains unconfirmed. What is confirmed is that OpenRouter has now named MiniMax, named the three forwarding hosts, and taken the Zero Data Retention label off the affected endpoints.
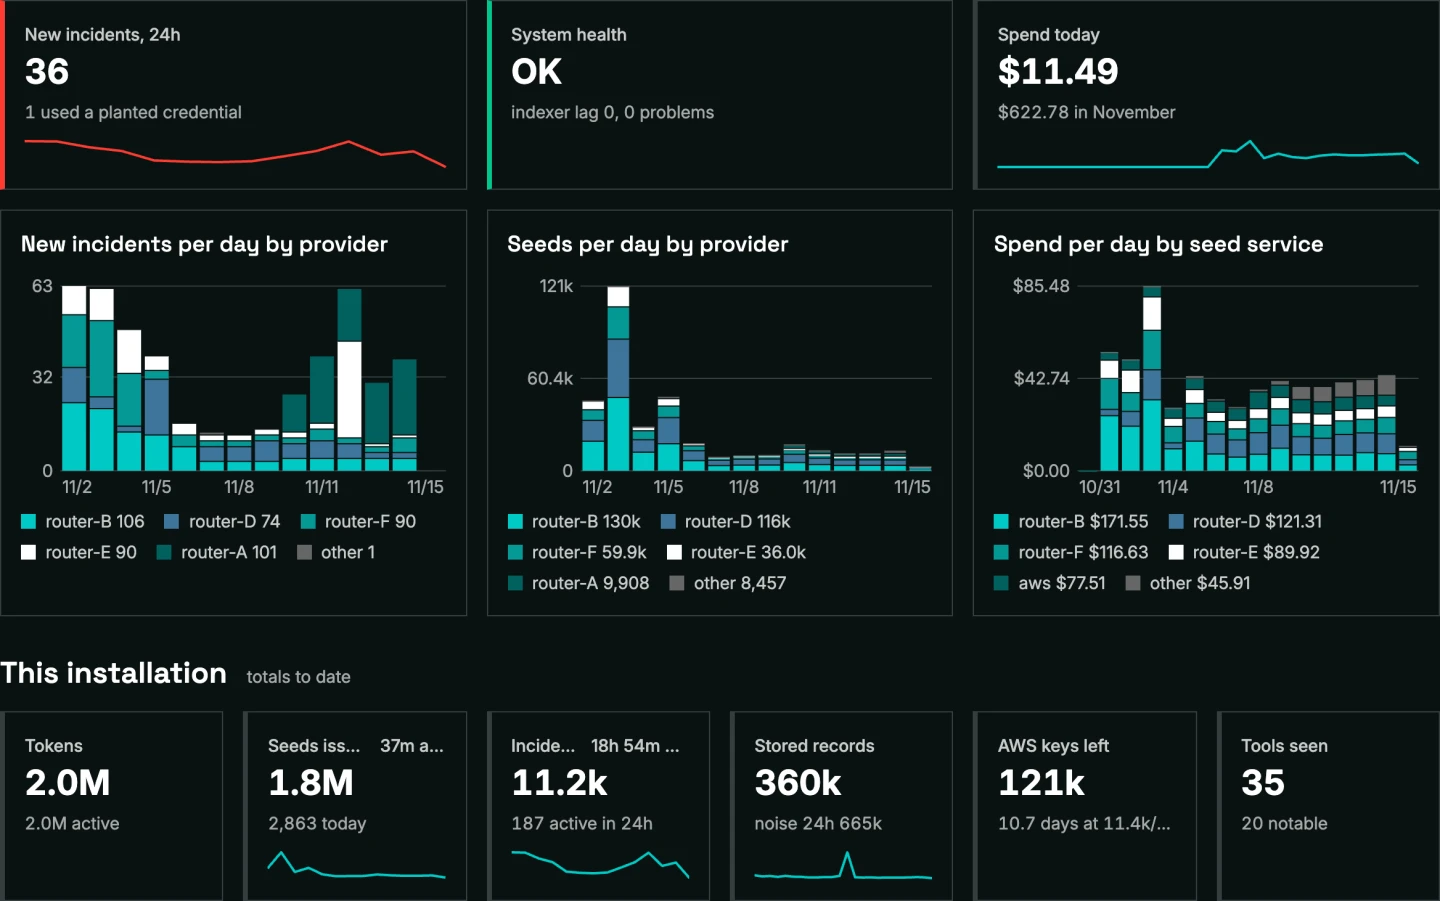
Dragos’s canary console tracked about two million seeded prompts. Image: Dragos
What Changed on OpenRouter
PrivacyAffairs, which reported the email on November 21, checked OpenRouter’s public model data the same morning and compared it with archived copies. In September, OpenRouter listed 13 hosts for MiniMax’s M3 model, including MiniMax itself, AtlasCloud, Novita and StreamLake. None of those four is listed for M3 now. On November 17, 35 of Novita’s endpoints carried OpenRouter’s Zero Data Retention label across DeepSeek, Kimi, GLM, Qwen and other models. On November 21, none did. The data policy entry for all four hosts now says they keep prompts, while other hosts running MiniMax models, such as DeepInfra, Fireworks and Together, still carry the label. The email does not say those hosts were affected.
The affected window may also run past October 22, the date in MiniMax’s explanation. The small tech site RuntimeWire, which reported the notice first at 03:54 UTC on November 21, said its own copy covered 80 requests sent through four hosts between October 15 and November 12, and told it to rotate any secrets in them. About 40 minutes after that report, a Hacker News user posted the full email, and researcher Max Woolf confirmed he had received the same message independently.
What Users Should Do
Anyone who sent MiniMax prompts through OpenRouter should treat those prompts as read. That means rotating any password, API key or token that appeared in them, and revoking it rather than only adding a new one. The test links were opened even though the test keys were never used, so signed download links, webhook URLs, password reset links and internal hostnames in a prompt are just as readable as a key.
OpenRouter lets customers require Zero Data Retention per request or for a whole account, and choose which providers may serve them. This case shows the label is the host’s promise, and the router cannot see what happens after a request leaves it. As Moore put it in the Dragos study, “a privacy flag only binds the first hop.”